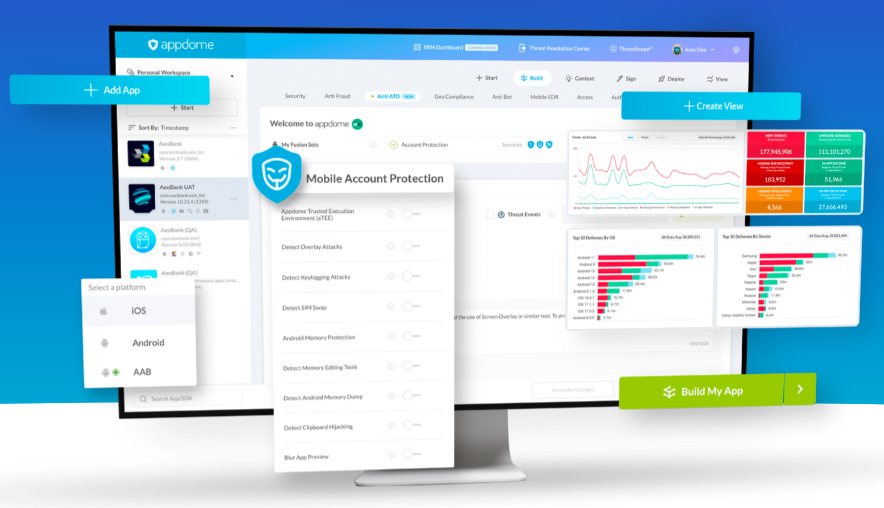

Appdome has unveiled 32 new AI-powered dynamic defense plugins, significantly expanding its Mobile Account Protection suite to combat rising threats of Account Takeovers (ATOs) and On-Device Fraud (ODF).
These new tools are tailored to help mobile brands protect user identities, secure account creation, and safeguard transactions against increasingly advanced malware targeting mobile commerce and other app experiences.
Like all of Appdome’s AI-Native protections, the new plugins can be implemented without writing code, integrating SDKs, or deploying servers—offering seamless integration through the Appdome platform.
“Account takeovers are one of the biggest risks mobile businesses face today,” said Jason Bloomberg, Managing Director at Intellyx. “Appdome’s approach secures user identities and account data throughout the entire customer journey—before damage can occur.”
Why ATOs are rising—and harder to detect
The growing complexity of mobile apps—especially Super Apps—and the use of AI by bad actors have lowered the bar for attackers. New tools now allow fraudsters to exploit mobile identities and account data at virtually any stage, from download to authentication. Traditional fraud solutions often detect threats after the fact, using common attack signatures, leaving mobile apps vulnerable during key operations.
Appdome takes a different approach by embedding security directly within the execution layer of the app. If a threat is detected, its AI-Native plugins can automatically block the attack or alert the app in real-time—delivering proactive protection before damage occurs.
“The weak point in ATO defense lies in unprotected communication paths between users and services—such as APIs, IPCs, and CPCs,” said Appdome CEO and co-creator Tom Tovar. “Attackers already exploit these to steal credentials, tokens, memory states, and more. Our plugins bring protection to the execution layer, where it’s most needed.”
Breaking down the 32 new plugins
Appdome’s expanded protection suite introduces three main categories of defense:
- Trusted Execution Environment (TEE): Creates a secure space within Android and iOS apps to handle sensitive identity, transaction, and account data. It protects memory, processes, APIs, IPCs, and more—while offering secure session management and secret storage.
- Dynamic Memory Protection: Defends against in-memory attacks where hackers attempt to access, manipulate, or extract credentials and other sensitive data.
- Identity Theft Prevention: Stops threats like SIM swapping, keylogging, overlay attacks, clipboard hijacks, and other techniques aimed at stealing user identities.
Setting a new standard in mobile fraud prevention
These new AI-driven tools offer layered, choice-based protection with no-code delivery—enabling brands to customize their defenses based on unique business needs.
The plugins integrate with Appdome’s Threat-Events™ and ThreatScope platforms, which provide real-time attack insights, user experience control, and actionable threat analytics. Brands can tailor their responses with branded workflows and messaging, and track threat activity across the customer journey.
“Most mobile apps simply aren’t equipped to handle today’s sophisticated on-device threats,” said Chris Roeckl, Appdome’s Chief Product Officer. “We’re moving into a new era where legacy solutions can’t keep up. Our platform allows mobile brands to take control—and go deeper.”
With this launch, Appdome sets a new benchmark in mobile security, offering businesses the tools to prevent account takeovers before they start—directly inside the app.