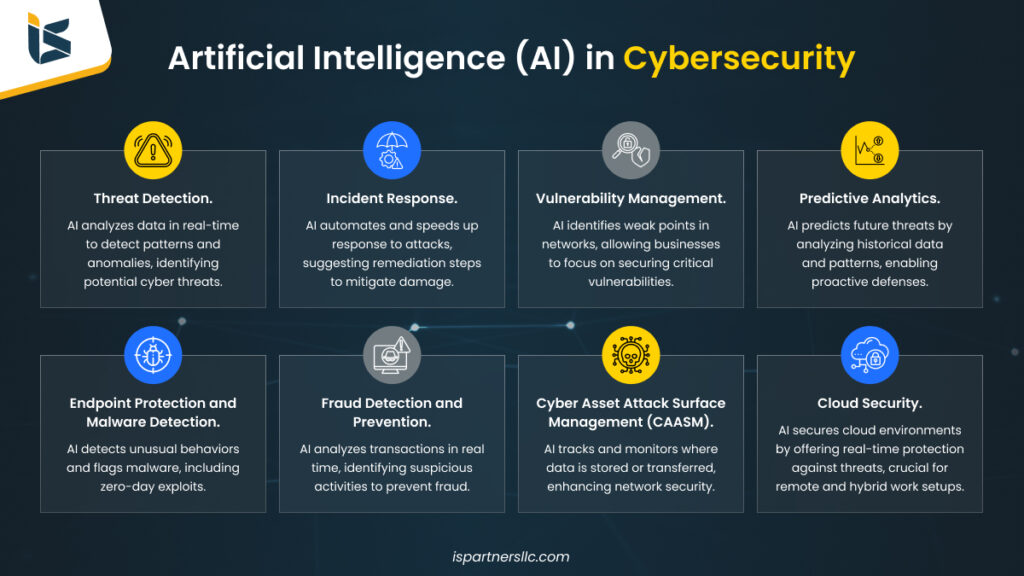

The race to adopt enterprise AI is rapidly reshaping the cloud—and not in a good way for security teams. According to the newly released 2025 State of Cloud Security Report from Palo Alto Networks, AI-driven workloads are dramatically expanding the cloud attack surface, leaving organizations struggling to keep up with a surge in threats, insecure code, and increasingly sophisticated attacks.
The report paints a stark picture of today’s cloud reality. Nearly every organization surveyed—99%—experienced at least one attack targeting AI applications or services in the past year. As companies scale cloud infrastructure to support AI initiatives, attackers are following closely, exploiting gaps across APIs, identities, and network access faster than security teams can respond.
Compounding the problem is the explosive rise of GenAI-assisted “vibe coding.” While it accelerates development, it is also flooding cloud environments with vulnerable code. Although more than half of organizations now ship code on a weekly basis, fewer than one in five can remediate vulnerabilities at the same pace. The result is a growing backlog of unaddressed risks accumulating across production environments.
Elad Koren, vice president of product management for Cortex at Palo Alto Networks, warned that many organizations are unintentionally creating new doors for attackers as they scale AI. Traditional cloud security approaches, he said, are no longer enough in an environment where threats move at machine speed and defenses rely on fragmented tools and slow, manual processes. To keep up, security teams must evolve beyond static visibility and embrace platforms that can operate as fast as their adversaries.
Based on insights from more than 2,800 security leaders and practitioners across 10 countries, the report highlights several alarming trends reshaping cloud risk.
Attackers are shifting their focus to the core layers of cloud infrastructure, with APIs, identity systems, and lateral movement emerging as prime targets. API-related attacks alone surged by 41%, fueled by the growing reliance of agentic AI systems on interconnected services. Identity and access management remains a critical weak point, with over half of respondents citing overly permissive access controls as a major vulnerability that enables credential theft and data exfiltration.
Lateral movement inside cloud environments continues to pose a serious threat. Nearly a third of organizations flagged unrestricted network access between workloads as a growing risk, allowing attackers to turn a single breach into a widespread compromise.
The report also underscores the operational strain caused by tool sprawl. Organizations now juggle an average of 17 cloud security tools from multiple vendors, creating blind spots, fragmented data, and slower response times. Almost all respondents said consolidating their cloud security stack is now a top priority. Siloed workflows between cloud security teams and security operations centers further delay remediation, with many incidents taking more than a full day to resolve.
There is, however, strong agreement on what must change. A large majority of organizations believe cloud, application, and SOC security must be fully integrated to be effective. As attackers increasingly weaponize AI to accelerate and automate attacks, the report stresses that defending modern cloud environments requires end-to-end protection that combines proactive risk reduction with real-time incident response—without the friction of disconnected tools.
In an era where AI is both a powerful enabler and a dangerous accelerant for cyber threats, the message from the report is clear: cloud security must move at the speed of AI, or risk falling dangerously behind.